THE LINUX FOUNDATION PROJECTS
Category

News

42dot Achieves Conformance with ISO/IEC 5230

By Conformance, News

42dot has achieved conformance with ISO/IEC 5230, the international standard for open source license compliance developed through the OpenChain Project.

ISO/IEC 5230 provides a framework for organizations to establish and maintain effective open source compliance programs. Conformance demonstrates that an organization has implemented the processes and controls needed to manage open source software and associated license obligations in a consistent and reliable manner.

As part of this effort, 42dot strengthened its open source governance framework and enhanced collaboration across engineering, legal, and other key functions. The result is a scalable compliance program that supports the responsible use of open source software throughout the organization.

Open source software plays a critical role in modern mobility solutions, including software-defined vehicles and connected mobility platforms. As these technologies continue to evolve, effective governance helps organizations manage software supply chain risks while enabling innovation and collaboration.

“Achieving ISO/IEC 5230 conformance marks an important milestone for 42dot,” said a company representative. “The work involved in reaching this standard has helped us further mature our internal processes and establish a strong foundation for the continued growth of our open source activities.”

This achievement also reinforces the importance of transparency, accountability, and effective software supply chain management as open source software continues to power the next generation of mobility technologies.

42dot joins a growing community of organizations around the world that have adopted ISO/IEC 5230 as a benchmark for open source compliance and software supply chain management.

OSCHINA Joins the OpenChain Partner Program to Advance Software Supply Chain Security

By Featured, News

OSCHINA has officially joined the OpenChain Partner Program, an initiative of OpenChain under the Linux Foundation dedicated to improving trust, security, and compliance in software supply chains worldwide.

As one of China’s leading open-source and developer platform providers, OSCHINA will contribute its expertise in software supply chain security, open-source governance, and developer ecosystems while collaborating with organizations around the world to advance industry best practices and international standards.

OpenChain, established by the Linux Foundation in 2015, brings together companies, industry groups, and public sector organizations to develop practical standards and reference materials that support effective open-source compliance and software supply chain management.

Strengthening Software Supply Chain Security

Over the years, OSCHINA has developed comprehensive software supply chain security capabilities through its developer ecosystem and enterprise R&D platforms. The company has built a full-lifecycle framework that addresses security requirements across source code management, component analysis, build processes, software delivery, and runtime operations.

Its platform integrates technologies such as Static Application Security Testing (SAST), Software Composition Analysis (SCA), reachability analysis, and intelligent auditing to help organizations identify vulnerabilities, manage open-source risks, and improve license compliance. Through deep integration with the Gitee DevOps platform, security checks can be incorporated directly into development workflows, providing continuous feedback throughout the software development lifecycle.

Supporting Global Standards and Industry Collaboration

OSCHINA currently operates two core platforms: the Gitee DevSecOps R&D Efficiency Platform and the Moark AI Platform.

As the designated operator of several national open-source initiatives in China, OSCHINA serves more than 18 million developers and supports organizations across industries including finance, government, manufacturing, and technology. Gitee DevSecOps has established a strong presence in enterprise software development environments, while Moark provides AI engineering capabilities spanning models, datasets, computing resources, and application development.

Participation in the OpenChain Partner Program provides an opportunity to contribute practical implementation experience to international discussions around software supply chain security while aligning with globally recognized approaches to open-source governance, compliance, and risk management.

Building a Trusted Open Source Ecosystem

“Joining the OpenChain Partner Program reflects our commitment to advancing trusted software supply chains and strengthening collaboration across the global open-source ecosystem,” said Ma Yue, Chairman of OSCHINA.

“From our origins as an open-source community and code hosting platform to our current role supporting enterprise software development and AI infrastructure, we have consistently focused on enabling innovation through open technologies. We look forward to working with the OpenChain community to promote best practices in compliance, security governance, and software supply chain management.”

Through its participation in OpenChain, OSCHINA aims to support organizations in establishing standardized and trustworthy software supply chain governance practices while contributing to the continued growth and security of the global open-source ecosystem.

norxs Technology Announces An OpenChain Conformant Program

By Featured, News

norxs Technology LLC has announced an OpenChain ISO/IEC 5230:2020 and ISO/IEC 18974:2023 conformant program, covering both open source license compliance and open source security assurance.

norxs is a functional safety and cybersecurity engineering firm working on systems where failure is not an option: EV powertrains, power distribution, and industrial controls. Its engagements span the full safety and security lifecycle — from hazard analysis and risk assessment (HARA) and threat analysis and risk assessment (TARA), through safety and security concepts, requirements decomposition, and implementation, to the verification, validation, and assessment evidence required for certification against ISO 26262, ISO/SAE 21434, IEC 61508, ISO 21448 (SOTIF), and the UN R155 / R156 regulations.

Safety-critical software is now built on open source, and the standards norxs’s clients answer to increasingly treat the software supply chain as part of the safety and security case itself. Conformance to ISO/IEC 5230 and ISO/IEC 18974 applies the same engineering discipline norxs brings to hardware and firmware — defined responsibilities, traceability, configuration management, and independent verification — to the open source it uses and ships. In practice this means knowing precisely which components are in a deliverable and the license obligations attached to each, alongside a defined process for identifying and responding to vulnerabilities across the product lifetime.

For norxs, license compliance and security assurance are two halves of a single obligation: providing customers an auditable account of the software they integrate. This maps directly onto the software supply chain expectations of ISO/SAE 21434 and UN R155, and norxs intends to contribute its safety-critical engineering perspective to the OpenChain community.

About norxs

norxs Technology LLC is a functional safety and cybersecurity engineering firm for safety-critical systems. It delivers hardware, firmware, and certification as a single team — built in from the first schematic rather than bolted on at the end — across EV powertrains, power distribution, and industrial controls.

norxs supports OEMs, Tier 1 suppliers, and industrial clients to standards including ISO 26262, IEC 61508, ISO/SAE 21434, ISO 21448 (SOTIF), UN R155 / R156, and ASPICE.

Learn More About norxs

JBViniol Joins OpenChain to Strengthen Practical Open Source Compliance

By News

JBViniol has officially joined the OpenChain project as an OpenChain Partner, reinforcing its long-standing commitment to practical and effective open source compliance. 

Founded in 2026, JBViniol advises organizations on intellectual property and technology law, with a particular focus on open source software. While the firm itself is newly established, its lawyers bring more than 25 years of experience supporting companies in navigating open source licensing, governance and compliance obligations.

JBViniol supports clients through a holistic approach that combines legal expertise with operational implementation. Its services include developing open source compliance programs, advising on governance structures and internal policies, supporting license compatibility analysis and risk mitigation, assisting with enforcement and dispute resolution, and integrating compliance practices into development and release workflows.

“​​Our lawyers have 25 years of experience advising clients on complying with open source license requirements, and we are delighted to bring this experience to the OpenChain Project,” said Dr. Till Jaeger, Partner at JBViniol.

A key challenge in open source compliance is not simply interpreting licenses in isolation, but applying legal requirements consistently across complex and rapidly evolving development environments. JBViniol helps organizations translate these obligations into structured and scalable workflows that can be implemented throughout the software lifecycle.

This work includes supporting clients in the review and interpretation of automated OSS license scan results. Typical review processes involve identifying open source components across codebases, verifying licenses against internal policies, assessing potential copyleft obligations, reviewing licensing information within source code, evaluating compatibility between licenses, analyzing technical implementation details, and defining appropriate remediation or approval actions.

By establishing structured and auditable compliance processes, organizations can move from isolated legal reviews toward scalable governance systems aligned with industry best practices.

By joining OpenChain, JBViniol aims to contribute its experience to a global community dedicated to improving transparency, trust, and consistency in the open source ecosystem. The firm believes that effective open source compliance requires both clear legal guidance and well-designed operational processes, and looks forward to advancing this approach within the OpenChain community.


About JBViniol

JBViniol is a law firm focused on intellectual property and technology law, with particular expertise in open source software compliance and governance. The firm advises organizations on the legal and organizational aspects of open source adoption, helping clients implement practical compliance programs and manage software supply chain risks effectively.


About OpenChain

The OpenChain Project has an extensive global community of over 1,000 companies collaborating to make the supply chain quicker, more effective and more efficient. It maintains OpenChain ISO/IEC 5230, the international standard for open source license compliance programs and OpenChain ISO/IEC 18974, the industry standard for open source security assurance programs.


About The Linux Foundation

The Linux Foundation is the world’s leading home for collaboration on open source software, hardware, standards, and data. Linux Foundation projects are critical to the world’s infrastructure, including Linux, Kubernetes, Node.js, ONAP, PyTorch, RISC-V, SPDX, OpenChain, and more. The Linux Foundation focuses on leveraging best practices and addressing the needs of contributors, users, and solution providers to create sustainable models for open collaboration. For more information

OpenChain Newsletter #86

By Featured, News

The OpenChain Newsletter provides a monthly summary of our work. It contains an overview of what we are doing to build trust around license compliance and security in the open source supply chain. We accept suggestions and ideas. Feel free to mail us at any time.

This month’s update highlights significant momentum in global adoption, alongside a big ‘Open Chain and Friends’ event with many tracks including Compliance, AI, CRA, Automotive, Education, and so on.

April has been a productive month for the OpenChain Project, with strong engagement across the Linux Foundation ecosystem, new working group activities, and continued progress on key deliverables that support software supply chain trust and compliance.

What happened in April? See the highlights below.


Engagement Across the Linux Foundation Ecosystem

In April, the OpenChain Executive Director participated in the Linux Foundation All Hands meeting alongside other open source projects.

This was a valuable opportunity to align with peer projects, exchange insights, and better understand how different communities are approaching shared challenges.

A key takeaway from the discussions is the growing importance of cross-project collaboration and communication. OpenChain is excited to further strengthen engagement with other initiatives and explore ways to collaborate more effectively across the ecosystem.


New OpenChain Business Operations Work Group

We are pleased to announce the formation of the OpenChain Business Operations Work Group.

The initial focus of the group is the Cyber Resilience Act (CRA), including:

  • Researching gaps in CRA compliance across diverse organizations
  • Identifying practical solutions to support implementation
  • Exploring how OpenChain can help companies prepare for and meet CRA requirements

This group will help connect real-world operational challenges with OpenChain standards and guidance, ensuring practical value for organizations navigating regulatory change. If  you would like to join this study group meeting (Biweekly on Monday), go to https://openchainproject.org/participate


Updated Adoption Resources

We have updated the OpenChain “Get Started” webpage to make it easier for organizations to understand and adopt OpenChain standards.

You can explore the updated resources here:
https://openchainproject.org/get-started


Welcome Renesas to the OpenChain Governing Board.

More information will come soon!

Closing Note

Thank you to all contributors and community members for your continued support and engagement. We look forward to continued collaboration and progress in the months ahead.

The Teoresi Group approach to open source governance

By Featured, News

Teoresi Group is an international engineering company that supports businesses in developing projects using cutting-edge technologies: from electric and autonomous vehicles to AI applied to medical diagnostics. With strong global expertise in engineering and machine learning, we focus on developing the intelligence layer that enables devices to operate autonomously and efficiently. 

Teoresi Group has been paying close attention to new technologies since 1987. So when open source software became impossible to ignore in products, in client deliverables, and in every layer of the engineering stack, the question was never whether to engage with it, but how to do so responsibly.

The honest answer to “why now?” is that the need became impossible to defer. In recent years, Teoresi’s work has shifted significantly toward turnkey projects. That shift changes the governance equation entirely. A service provider can rely on the client’s open source policies. A solution provider cannot. You need your own house in order.

“If you do not have governance, you carry all the risks we have been describing: legal exposure, security gaps, and compliance failures. The risk does not disappear because you did not look for it.” — Alberto Bertone, Teoresi Group FOSS Manager

A working group was established, including technical leads, legal experts, and project managers. The result, published by the end of 2025, was a Group-wide open source policy and procedure. All Teoresi Group companies are covered. The process runs from pre-sales through to delivery. Licence constraints are evaluated before commitments are made, codebases are scanned and inventoried during development, and a named FOSS Manager is accountable for the programme’s integrity across projects.

Training is already underway across the organisation. The goal is straightforward: every person who works with third-party code understands what that code requires of them, and why. Compliance that rests on understanding is durable. Compliance that rests only on instruction is not.

Teoresi has also declared its openness to contributing back to open source. This is a formal commitment under ISO/IEC 5230, the international standard with which the programme is aligned. Research projects and innovation initiatives offer natural pathways. Open source is not something Teoresi simply consumes; it is something the company intends to be a responsible part of.

The open source community made the tools we build on available to everyone. Managing that inheritance with care is not just a regulatory obligation. It is a professional one.

Webinar – Open Chain AI SBOM Self Certification & ISO 4200X

By ai, News, Webinar

About This Webinar:

This webinar explored the direction of OpenChain AI SBOM Self-Certification and its role in supporting responsible AI governance.

Xiaobo shared insights on transparency and explainability within ISO 42001, along with practical recommendations for implementing AI SBOM in alignment with ISO 42003. The session also covered key considerations and real-world approaches, supported by relevant materials.

Overall, the webinar highlighted how OpenChain AI SBOM can help organizations improve transparency, strengthen compliance, and enable more effective AI implementation.

Watch This Webinar:

Webinar – Open Chain AI SBOM Self Certification & ISO 4200X


OpenChain Newsletter #85

By Monthly Newsletter, News

The OpenChain Newsletter provides a monthly summary of our work. It contains an overview of what we are doing to build trust around license compliance and security in the open source supply chain. We accept suggestions and ideas. Feel free to mail us at any time.

This month’s update highlights significant momentum in global adoption, alongside a big ‘Open Chain and Friends’ event with many tracks including Compliance, AI, CRA, Automotive, Education, and so on.

New Executive Director on Board

We are pleased to announce that Mary Meixia Wang has joined the OpenChain Project as our new Executive Director.

We extend our sincere gratitude to our board members and contributors for their continued dedication and support. We would also like to recognize the pioneering leadership of Shane Coughlan whose vision and commitment have been instrumental in establishing OpenChain’s global success. For  more information, see https://openchainproject.org/news/2026/03/05/our-new-executive-director-for-openchain

New Adopters (ISO/IEC 5230, ISO 18974)

The ecosystem continues to expand with major industry players announcing conformance. This is a strong signal for supply chain managers to review their own vendor requirements.

Event

Open Chain and Friends event in Stuttgart

“OpenChain and Friends” is an in-person community event focused on open source software supply chain management, compliance, and collaboration. It’s organized by the OpenChain Project in partnership with local and international communities, such as The FOSS-LÄND Community. The event takes place in Stuttgart, Germany and gathers people working with open source across different industries.

for more information, see https://openchainproject.org/news/2025/12/09/openchain-and-friends-2026

For blogs, see https://openchainproject.org/news

SBOM Document Quality Guideline

We are announcing a public comment period for the SBOM Document Quality Guide that has been developed by the OpenChain SBOM Work Group.SBOM Document Quality Guide: https://lnkd.in/dhe3gFVW

Read Previous Newsletters:

Public Comment Period – SBOM Document Quality Guide – Ends 31st May 2026

By Featured, News

Public Comment Period – SBOM Document Quality Guide – Ends 31st May 2026Happening Now:We are announcing a public comment period for the SBOM Document Quality Guide that has been developed by the OpenChain SBOM Work Group.

Document: SBOM Document Quality GuideWhy This Is Happening:The OpenChain Project has a formal process for public comment periods related to important releases like the SBOM Document Quality Guide. These public comment periods signify that we have completed work on a topic, and now want to ensure people outside of the OpenChain Project and its work groups can provide additional input as needed. After the public comment period, we formally release the relevant document.How to write comments:We are accepting comments via our SBOM Work Group mailing list and through our monthly calls. The recommended way of providing feedback is via the mailing list.You can read the full process (and our other processes) here: https://lnkd.in/d7D4RmgNYou can find the URL for the mailing list here: https://lnkd.in/dEUf_tzKYou can find our SBOM Work Group calls (and all other OpenChain calls) list here: https://lnkd.in/dcA8pDR9A big thanks to @Norio Kobota and the whole of the OpenChain Project SBOM Work Group work on this document.

Beyond the Code: Fostering Connection and Collaboration at the Women in Open Source Networking Event @ OpenChain and Friends 2026

By Blogs, News

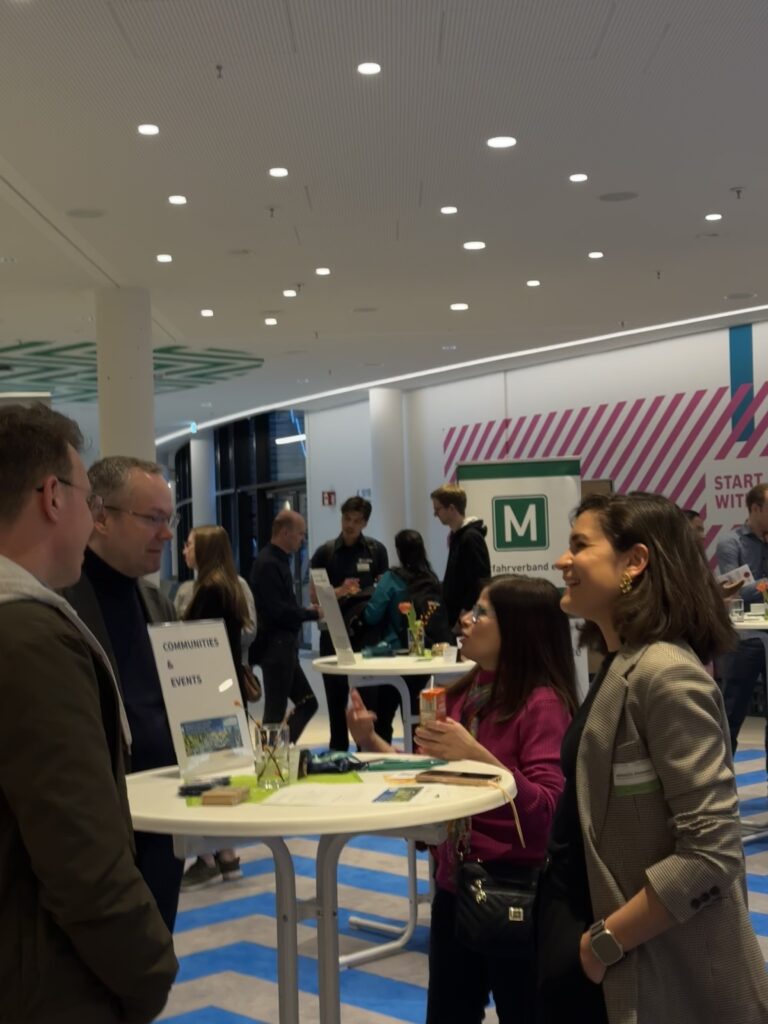
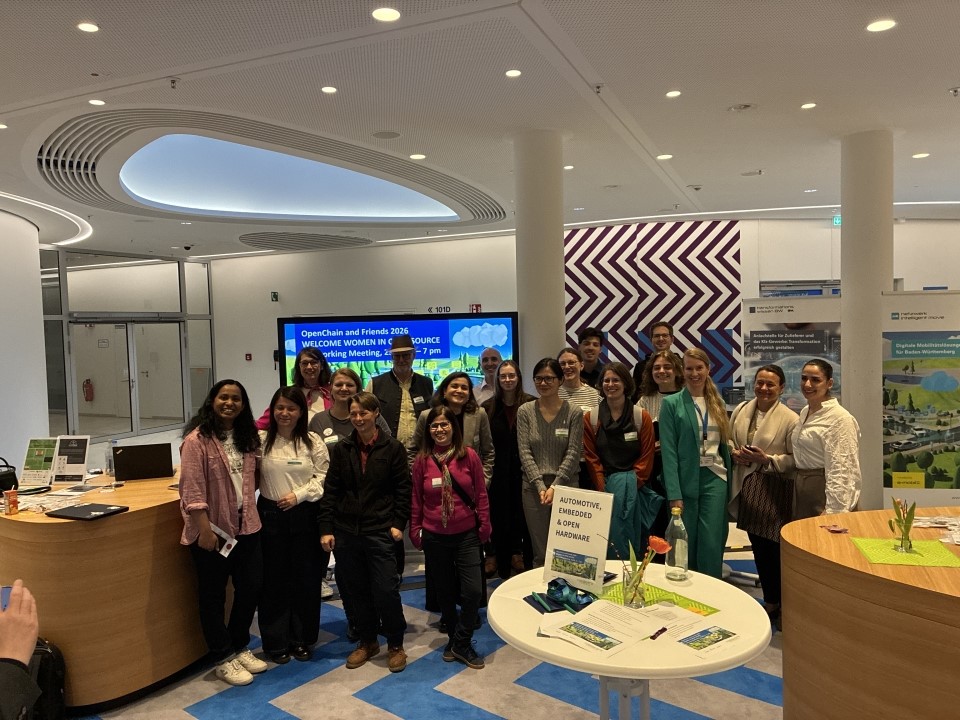
The energetic world of open source based not just on code, but on community, collaboration, and diverse perspectives. This was proved at a recent networking session designed specifically for women and allies in the open source ecosystem – an event that left attendees not only informed but deeply inspired. The session was organized as an open, moderated networking space, welcoming everyone who works with, contributes to, or is simply curious about Open Source. Its mission was to create environment for meaningful exchange, bridging technical, legal, business, and community perspectives.
Stepping into the event, I was experienced awesome energy in the place. It wasn’t just women interested in participating; it was a really diverse and welcoming group of people, and everyone seemed eager to chat even before the officially event started. People were already getting to know each other, swapping ideas, and just genuinely connecting. The format of the event encouraged dynamic interaction: two 30-minute discussion rounds were offered to the attendees. They had the freedom to choose themed tables that resonated most with their interests but aligned with broader topics of the Open Chain and Friends event. Participants could explore fresh perspectives, learn from each other, and build connections designed to last well beyond the evening. The diverse range of discussion themes included Communities, Compliance, Artificial Intelligence, Digital Sovereignty, Cybersecurity, Embedded and Open Hardware, Education and many others. Attendees quickly immersed themselves in discussions, sharing experiences and insights which led to dynamic and naturally flowing conversations.
It was fantastic to see so many different companies represented. This really helped us get diverse points of view and think about how we can all work together. The atmosphere was simply vibrant. By the end, the feedback was overwhelmingly positive. The enthusiasm was so high that discussions quickly turned to planning the next opportunity to meet, underscoring the success of building truly meaningful connections.

This event was a powerful reminder that while technology evolves rapidly, the human element – the desire to connect, learn, and collaborate – remains at the heart of the open source movement. A huge shout-out and thank you to the organizers and moderators – Adamantia Goulandris, Sarah Itt and Kurzmann Marcel – and special thank you for Women at Bosch for sponsoring this fantastic event!